Compound Labs
Menu
Get the newsletter
AGENTWIREGmpetrov/databerry, The no-code platform for building custom LLM AgentsNO-CODE LLM AGENTSFOUNDER MASTODONThe draft requires the repository evidenceNO REPOSITORY EVIDENCE, NO DRAFTSTACKTABStackTab updates price-watch subscriptions when users add or remove a watchWATCH REMOVAL UPDATES SUBSCRIPTIONCONTEXT WINDOWQwen3.8-27B model card now lists four modelsMODEL CARD LISTS FOUR MODELSFOUNDER LINKEDINAn unavailable source repository blocks carousel draftingNO SOURCE, NO CAROUSELSTANDUPThe Standup stubs Sharp and overrides npm for Cloudflare Workers buildsSTUBBED FOR WORKERS BUILDSAGENTWIRECodewhale: open-source Rust coding agent for your terminalOPEN-SOURCE RUST CODING AGENTCOMPOUND LINKEDINSkillWorks shares one score sentence across its badge and alertONE SCORE SENTENCE, TWO PATHSWIRECALLWireCall limits new device keys and validates 2-24 character leaderboard namesFIVE KEYS PER HOURTHE STANDUPnginx-ignition: unauthenticated admin account creationUNAUTHENTICATED ADMIN CREATIONCOMPOUND BLUESKYCompound Labs' roster now tracks all 125 instruction files125 FILES, FULLY ACCOUNTED FORTOOLDRIFTToolDrift records z-ai/glm-5.3-flash:batch leading Cline's rankingGLM-5.3-FLASH LEADS CLINETHE STANDUPHIGH: nginx-ignition has Unauthenticated Admin Creation via RaceUNAUTHENTICATED ADMIN CREATIONFOUNDER BLUESKYAgentwire checks sources and trips the lane after failuresTHREE FAILURES TRIP THE LANECARDCHASECardChase stops failed admin lookups from triggering fake payment retriesADMIN ERRORS STOP FAKE RETRIESCOMPOUNDCloudflare Python Workers are now generally availablePYTHON, GENERALLY AVAILABLEFOUNDER PEERLISTToolProof keeps its instrument tiles on one horizontally scrollable rowNINE TILES, ONE SCROLLING ROWSTILL-MORNINGSStill Mornings delays PostHog analytics and shares its promisePOSTHOG AFTER HYDRATION
Independent product R&D labFounded and run by Isaiah Kim, @kyisaiah47Newest commit Sep 22, 2026, QuorumFileNewest writing Sep 22, 2026Site changelog Sep 22, 2026
Sections
Sep 22, 20263 min read

BreachProbe scans a shipped app for database exposure

BreachProbe scans a shipped app's JavaScript, response headers, Supabase REST responses, and signed-in behavior, then shows what the app actually serves instead of stopping at a bundle search.


BreachProbe

The scan console

The main console shows one URL field, an authorization checkbox, and a "Scan free" control. It also keeps "NO ACCOUNT · NOTHING INSTALLED · READ-ONLY · ONE URL" beside the control.

The console sends the pasted address through the scan flow. It fetches the shipped page, reads its scripts, checks headers, probes database endpoints, and runs signed-in checks when the app supports them.
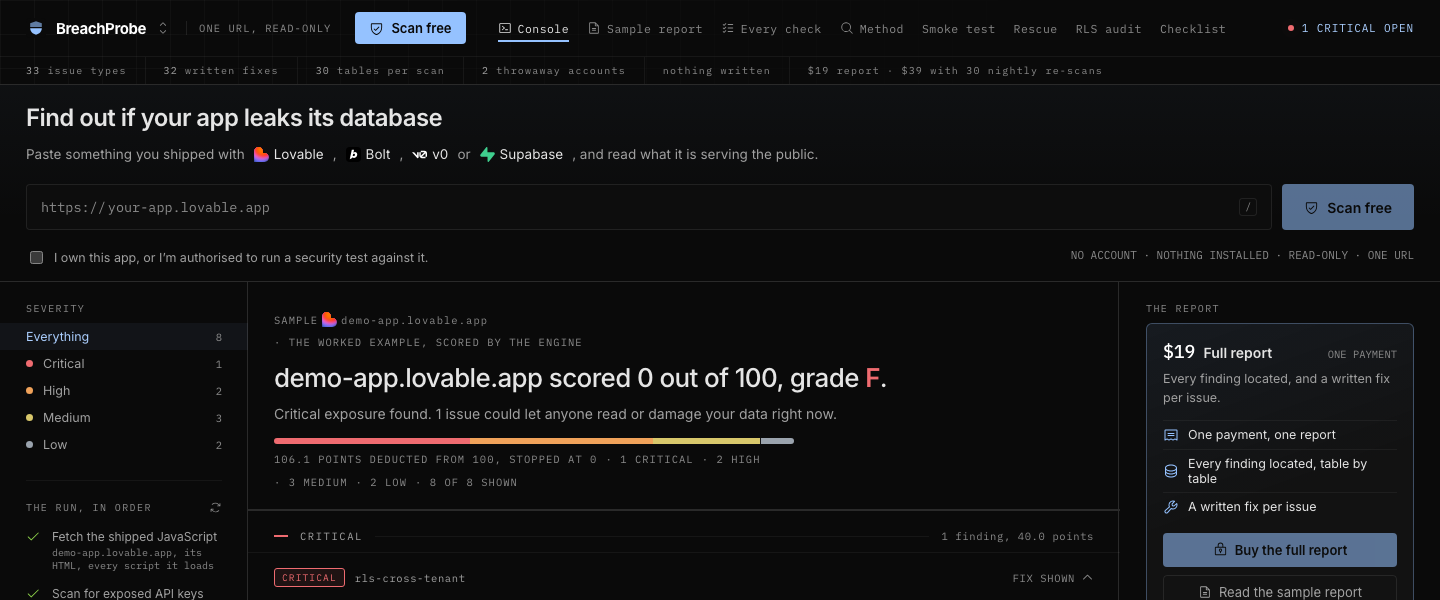
BreachProbe, The main console: SAMPLE demo-app.lovable.app · THE WORKED EXAMPLE, SCORED BY THE ENGINE demo-app.lovable.app scored out of 100, grade F.

The severity filter

The report rail shows Everything, Critical, High, Medium, and Low filters. The worked report marks one critical finding, two high findings, three medium findings, and two low findings.

The filter changes which findings remain in the report river. BreachProbe keeps each finding's title, severity, evidence source, and written fix attached to the same result.
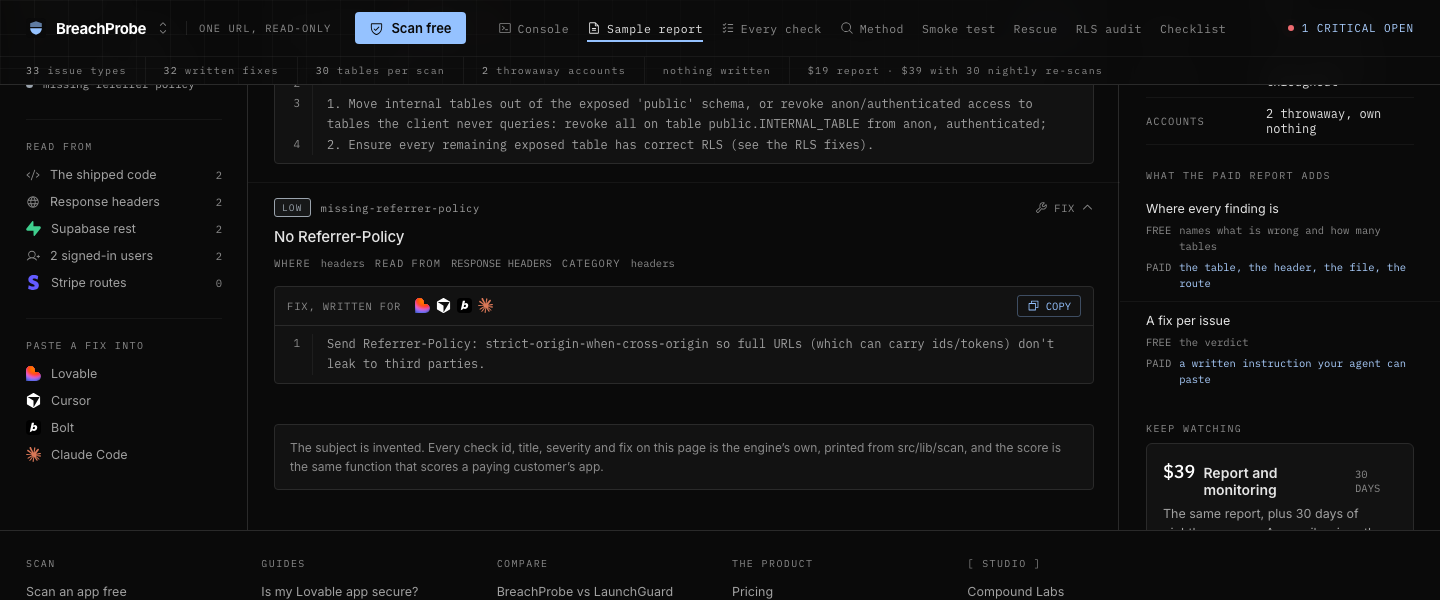
BreachProbe, Sample report: The subject is invented. Every check id, title, severity and fix on this page is the engine’s own, printed from src/lib/

The run order

The console lists the scan in order: shipped JavaScript, exposed API keys, Supabase REST endpoints, security headers, broken-auth patterns, Stripe routes, and two signed-in users.

That order separates passive inspection from behavior tests. The scan reads code and headers first, then checks whether tables answer anonymous requests and whether one signed-in user can read another user's rows.
BreachProbe, About: The release figures on this page are counted from this product's own commit history by a script, and a build gate re-run

The sample report

The sample report shows a failing worked example with a critical row-level security finding. It identifies three affected tables and says the read crossed two signed-in users.

The report turns that result into a written SQL fix. It tells the reader to compare auth.uid() with the row owner column and to verify that a fresh user reads zero rows after the policy changes.
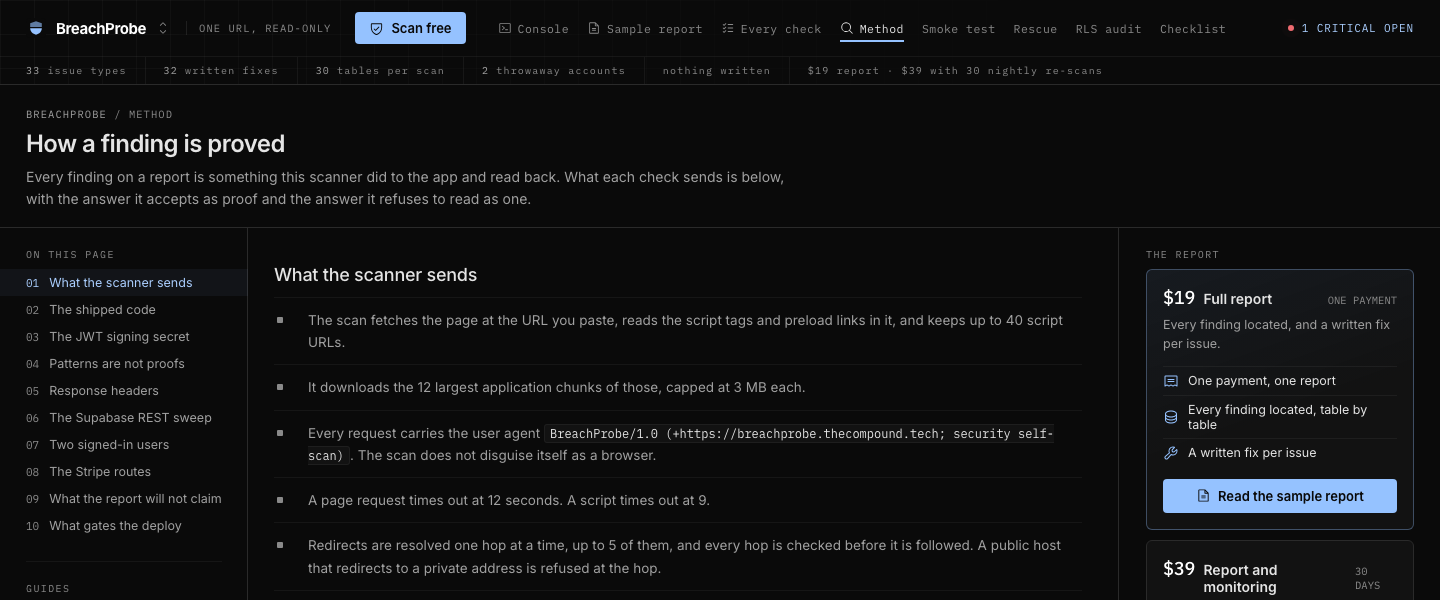
BreachProbe, Method: BREACHPROBE / METHOD How a finding is proved Every finding on a report is something this scanner did to the app and read

The method page

The method page explains what each probe sends and what answer counts as proof. It separates shipped-code patterns, response headers, Supabase REST reads, signed-in isolation checks, and Stripe route checks.

The JWT signing-secret check uses a different standard from a string match. BreachProbe recomputes the HS256 signature of the app's own public key, so a random 40-character build value does not become a finding.
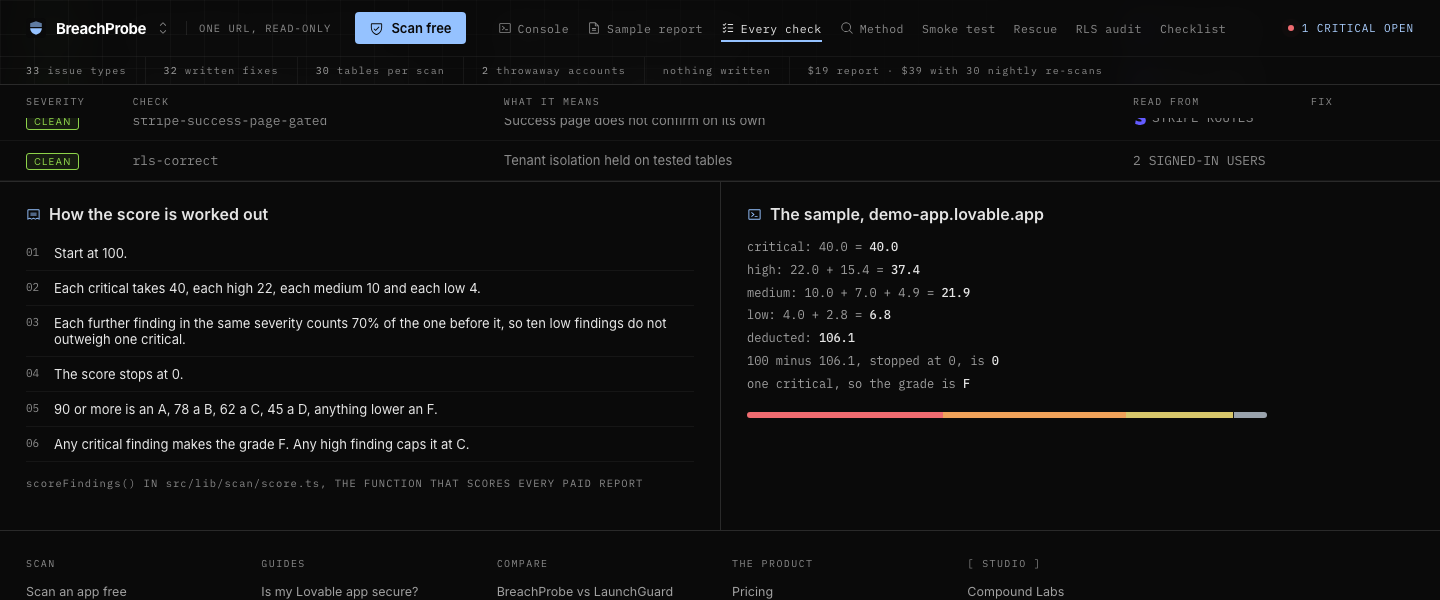
BreachProbe, Every check: 01 Start at 100. 02 Each critical takes 40, each high 22, each medium 10 and each low 4. 03 Each further finding in the

The scan error state

The console keeps the four operating terms visible when a scan fails, then places the error on its own row underneath. The failed state no longer replaces the read-only and no-account explanation.

I changed ScanBar so the assurance text stays mounted independently of the error message. I also added the JWT signing-secret check to the deploy checks after the first implementation swallowed an ES module require error and reported a clean result for every fixture.

All writing

Alongside